Your privacy policy has a December deadline, and it lands on your website

Get Your Free Website Audit
($3,000 Value)
- Uncover performance issues
- Identify SEO opportunities
- Security gaps, and quick wins
Last updated 12 October 2026.
The short version
- From 10 December 2026, Australian privacy policies must disclose the automated decisions a business makes about people.
- The scope is far broader than AI. Spreadsheets, rule-based logic and ordinary software all count.
- Most of the tools caught by this sit in the marketing stack, not the IT stack.
- A human reviewing the output does not take a tool out of scope.
- The obligation sits with the business using the tool, not the vendor who built it.
On 30 September 2026, the Office of the Australian Information Commissioner published its final guidance on a new transparency obligation. It takes effect on 10 December 2026.
Plenty of law firms have written about what the rule says. Fewer people have written about where it actually lands, which is on the website and the marketing stack rather than the legal department.
That is the part we are useful for, so that is what this article covers.
What is changing
Three new Australian Privacy Principles, APP 1.7 to 1.9, were added by the Privacy and Other Legislation Amendment Act 2024. They commence on 10 December 2026.
From that date, if your business uses a computer program to make, or to substantially help make, decisions that significantly affect people, your privacy policy has to say so.
The three-limb test
You are in scope when all three of these are true.
- You have arranged for a computer program to make a decision, or to do something substantially and directly related to making one. This covers tools you built, tools you bought, packaged software you customised, and outputs you rely on for advice.
- The decision could reasonably be expected to significantly affect an individual’s rights or interests.
- Personal information about that individual is used in running the program.
What counts as a “computer program”
This is where most businesses underestimate the rule. The OAIC’s guidance is deliberately broad. It covers:
- Rule-based processes and conditional logic
- Ordinary software, including spreadsheet automation
- Machine learning and predictive scoring models
- Generative AI, including chatbots
A “decision” is also wider than it sounds. It includes deliberately acting, refusing to act, and failing to act.
Human review does not automatically save you. The guidance is clear that sign-off alone is not enough. If the program’s output is a key factor in the decision, it is in scope. What may help is interrogating the output, narrowing the parameters it runs on, and documenting the occasions where you departed from its recommendation.
Why this lands on marketing, not legal
The OAIC published a non-exhaustive list of decisions likely to significantly affect someone. Several of them describe things that live on a website.
The list includes recruitment screening, differential or personalised pricing on significant goods and services, loan or credit decisions, insurance eligibility, education and training admission, eligibility for government benefits or housing, prioritising health or disability services, facial recognition for watchlists, AI-generated employee performance reports, scholarship and grant decisions, and programmatic advertising for significant goods or services.
Two of the worked examples in the guidance are worth knowing. One confirms that small price differences count when they add up to a meaningful amount over time. Another confirms that ad targeting which limits who sees a job advertisement is in scope.
The tools on your site that are probably caught
Here is the practical version. These are the website and marketing components we see most often, and why they may fall inside the test.
| What it is | Why it may be in scope |
|---|---|
| Instant quote or pricing calculator | Produces a personalised price from personal information. Personalised pricing on significant goods is on the OAIC list. |
| Lead scoring in your CRM | Decides who gets a callback and who does not. Failing to act is a decision. |
| Chatbot that qualifies or routes enquiries | Generative AI is named explicitly. Triage that closes off access to a service is a decision. |
| Careers page screening | Knockout questions, CV parsing and ranking. Recruitment screening is on the list. |
| Eligibility or pre-assessment widgets | Common on finance, insurance and health sites. Eligibility decisions are named directly. |
| Audience building for paid media | Built from first-party site data. Programmatic advertising for significant goods is on the list. |
| Personalisation engines | Different visitors see different offers, prices or products based on their data. |
| Booking systems that allocate priority | Where the queue position affects access to a service that matters. |
Not every one of these will be in scope for every business. The point is that the inventory starts on your website, and in most organisations nobody has written that inventory down.
One more thing that catches people out. Systems run on your behalf by an agency, outsourcer or service provider are caught too. Your vendor should give you the high-level information you need, but the obligation stays with you.
Build your inventory in ten minutes
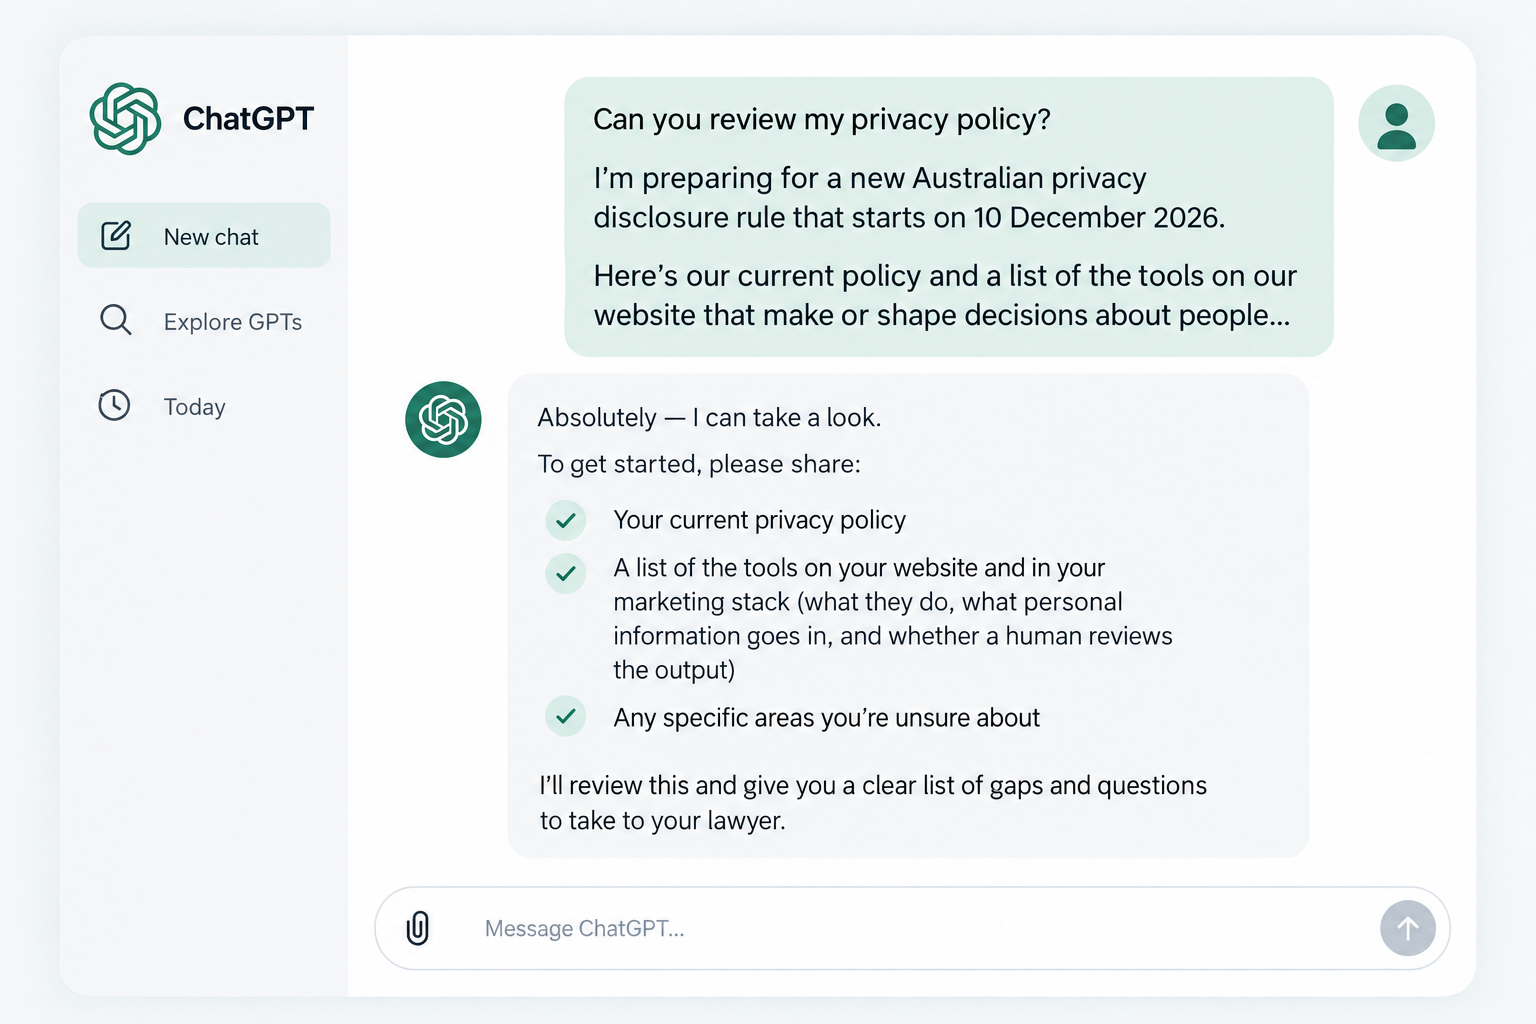
This is the prompt we use to find the gap between what a privacy policy says and what a website actually does. Paste it into ChatGPT or Claude with your policy and your tool list.
You are helping me prepare for a new Australian privacy
disclosure rule that starts on 10 December 2026.

From that date, a privacy policy must disclose:
1. The kinds of personal information used by computer programs
   that make, or substantially help make, decisions about people.
2. The kinds of decisions those programs make on their own.
3. The kinds of decisions where a program does something
   substantially and directly related to the decision.

Scope is broad. Spreadsheets, rule-based tools, machine learning
and generative AI all count. A human reviewing the output does
not take a tool out of scope. The obligation sits with the
business using the tool, not the vendor.

Our current privacy policy:
[PASTE YOUR POLICY]

Tools on our website and in our marketing stack that make or
shape decisions about people:
[LIST EACH ONE: what it does, what personal information goes in,
whether a human reviews the output]

Do three things:
1. List every tool that is not described anywhere in the policy.
2. For each gap, say which of the three points above is missing.
3. Flag any tool you are unsure about, and say what you would
   need to know to decide.

Do not write policy wording. Do not give legal advice.
Give me a list I can take to a lawyer.
The output is a shortlist to take to your lawyer. It is not legal advice and it is not a substitute for one.
What your privacy policy has to say
APP 1.8 requires three things in the policy:

Slow website wasting your marketing spend?
- Uncover performance issues
- Identify SEO opportunities
- Security gaps, and quick wins
- The kinds of personal information used in operating those programs.
- The kinds of decisions made solely by a program.
- The kinds of decisions where a program does something substantially and directly related to the decision.
How much detail
Less than people expect, and the guidance is helpful here. The test is whether an ordinary person can understand how their information is handled. You are told to avoid granular technical detail and to group categories together, as long as the grouping still means something to a reasonable person.
Two things to be careful about. Sensitive information, such as health data or biometric templates, should be clearly visible rather than buried in a category. And if you are unsure whether something is in scope, the guidance says to take the cautious path and disclose it.
The commercial-in-confidence exception
Genuinely commercially sensitive information and trade secrets are excluded. The guidance sets out three questions that help decide: is the information unique to you and does it lose value if known, does it give you a competitive edge, and would an arm’s-length buyer pay for it?
Two things are explicitly not excluded. The bare fact that personal information powers a tool is not commercially sensitive. Neither is information you would simply rather not publish because it might attract criticism or embarrassment.
What this is not
It is worth being clear about the limits, because a few write-ups have overstated them.
- This is a transparency obligation. It does not give anyone a right to contest an automated decision.
- There is no requirement to notify individuals directly. The disclosure goes in the policy.
- It is not a copy of GDPR Article 22. Australia’s version leaves out the right not to be subject to automated decision-making and the human intervention safeguards.
A second tranche of reform has been flagged but deferred, with no timetable. It is expected to include privacy impact assessments for high-risk activities, a right to an explanation of automated decisions, and a fair and reasonable test for data handling regardless of consent. Worth building for, not worth waiting for.
What happens if you miss it
The 2024 amendments added lower penalty tiers specifically so the regulator can act on administrative breaches without running a major case.
Breaches of APP 1, which is the privacy policy principle, sit within the infringement notice regime. For a body corporate that is up to $19,800 per contravention, rising to $66,000 for a publicly listed company. Above that sit a civil penalty tier of up to $330,000 for specified APP breaches, a mid-tier of $3.3 million for an interference with privacy, and the serious interference tier of up to $50 million.
The realistic risk for most businesses is not a headline fine. It is a complaint, a compliance notice, and a scramble.
What to do in the next eight weeks
- Build the inventory. Walk your website and your marketing stack and list every tool that makes or shapes a decision about a person. Use the prompt above if it helps.
- Record what goes in. For each tool, note the personal information it uses and whether a human reviews the output.
- Ask your vendors. Anything run on your behalf is still your obligation. Request the high-level description you need, in writing.
- Run the three-limb test on each one, and mark the uncertain ones rather than dropping them.
- Hand the list to whoever owns your privacy policy. They cannot write the disclosure without it, and this is the step that takes the longest.
- Keep the inventory. It becomes a living document, because every new tool added to the site changes the answer.
A note on what this is. WP Creative is a web performance agency, not a law firm. This article explains what changed and helps you find the tools on your website that may be affected. It is general information, not legal advice. Take your inventory to a lawyer before you rewrite your privacy policy.
Sources and further reading

Get Your Free Website Audit
($3,000 Value)
- Uncover performance issues
- Identify SEO opportunities
- Security gaps, and quick wins